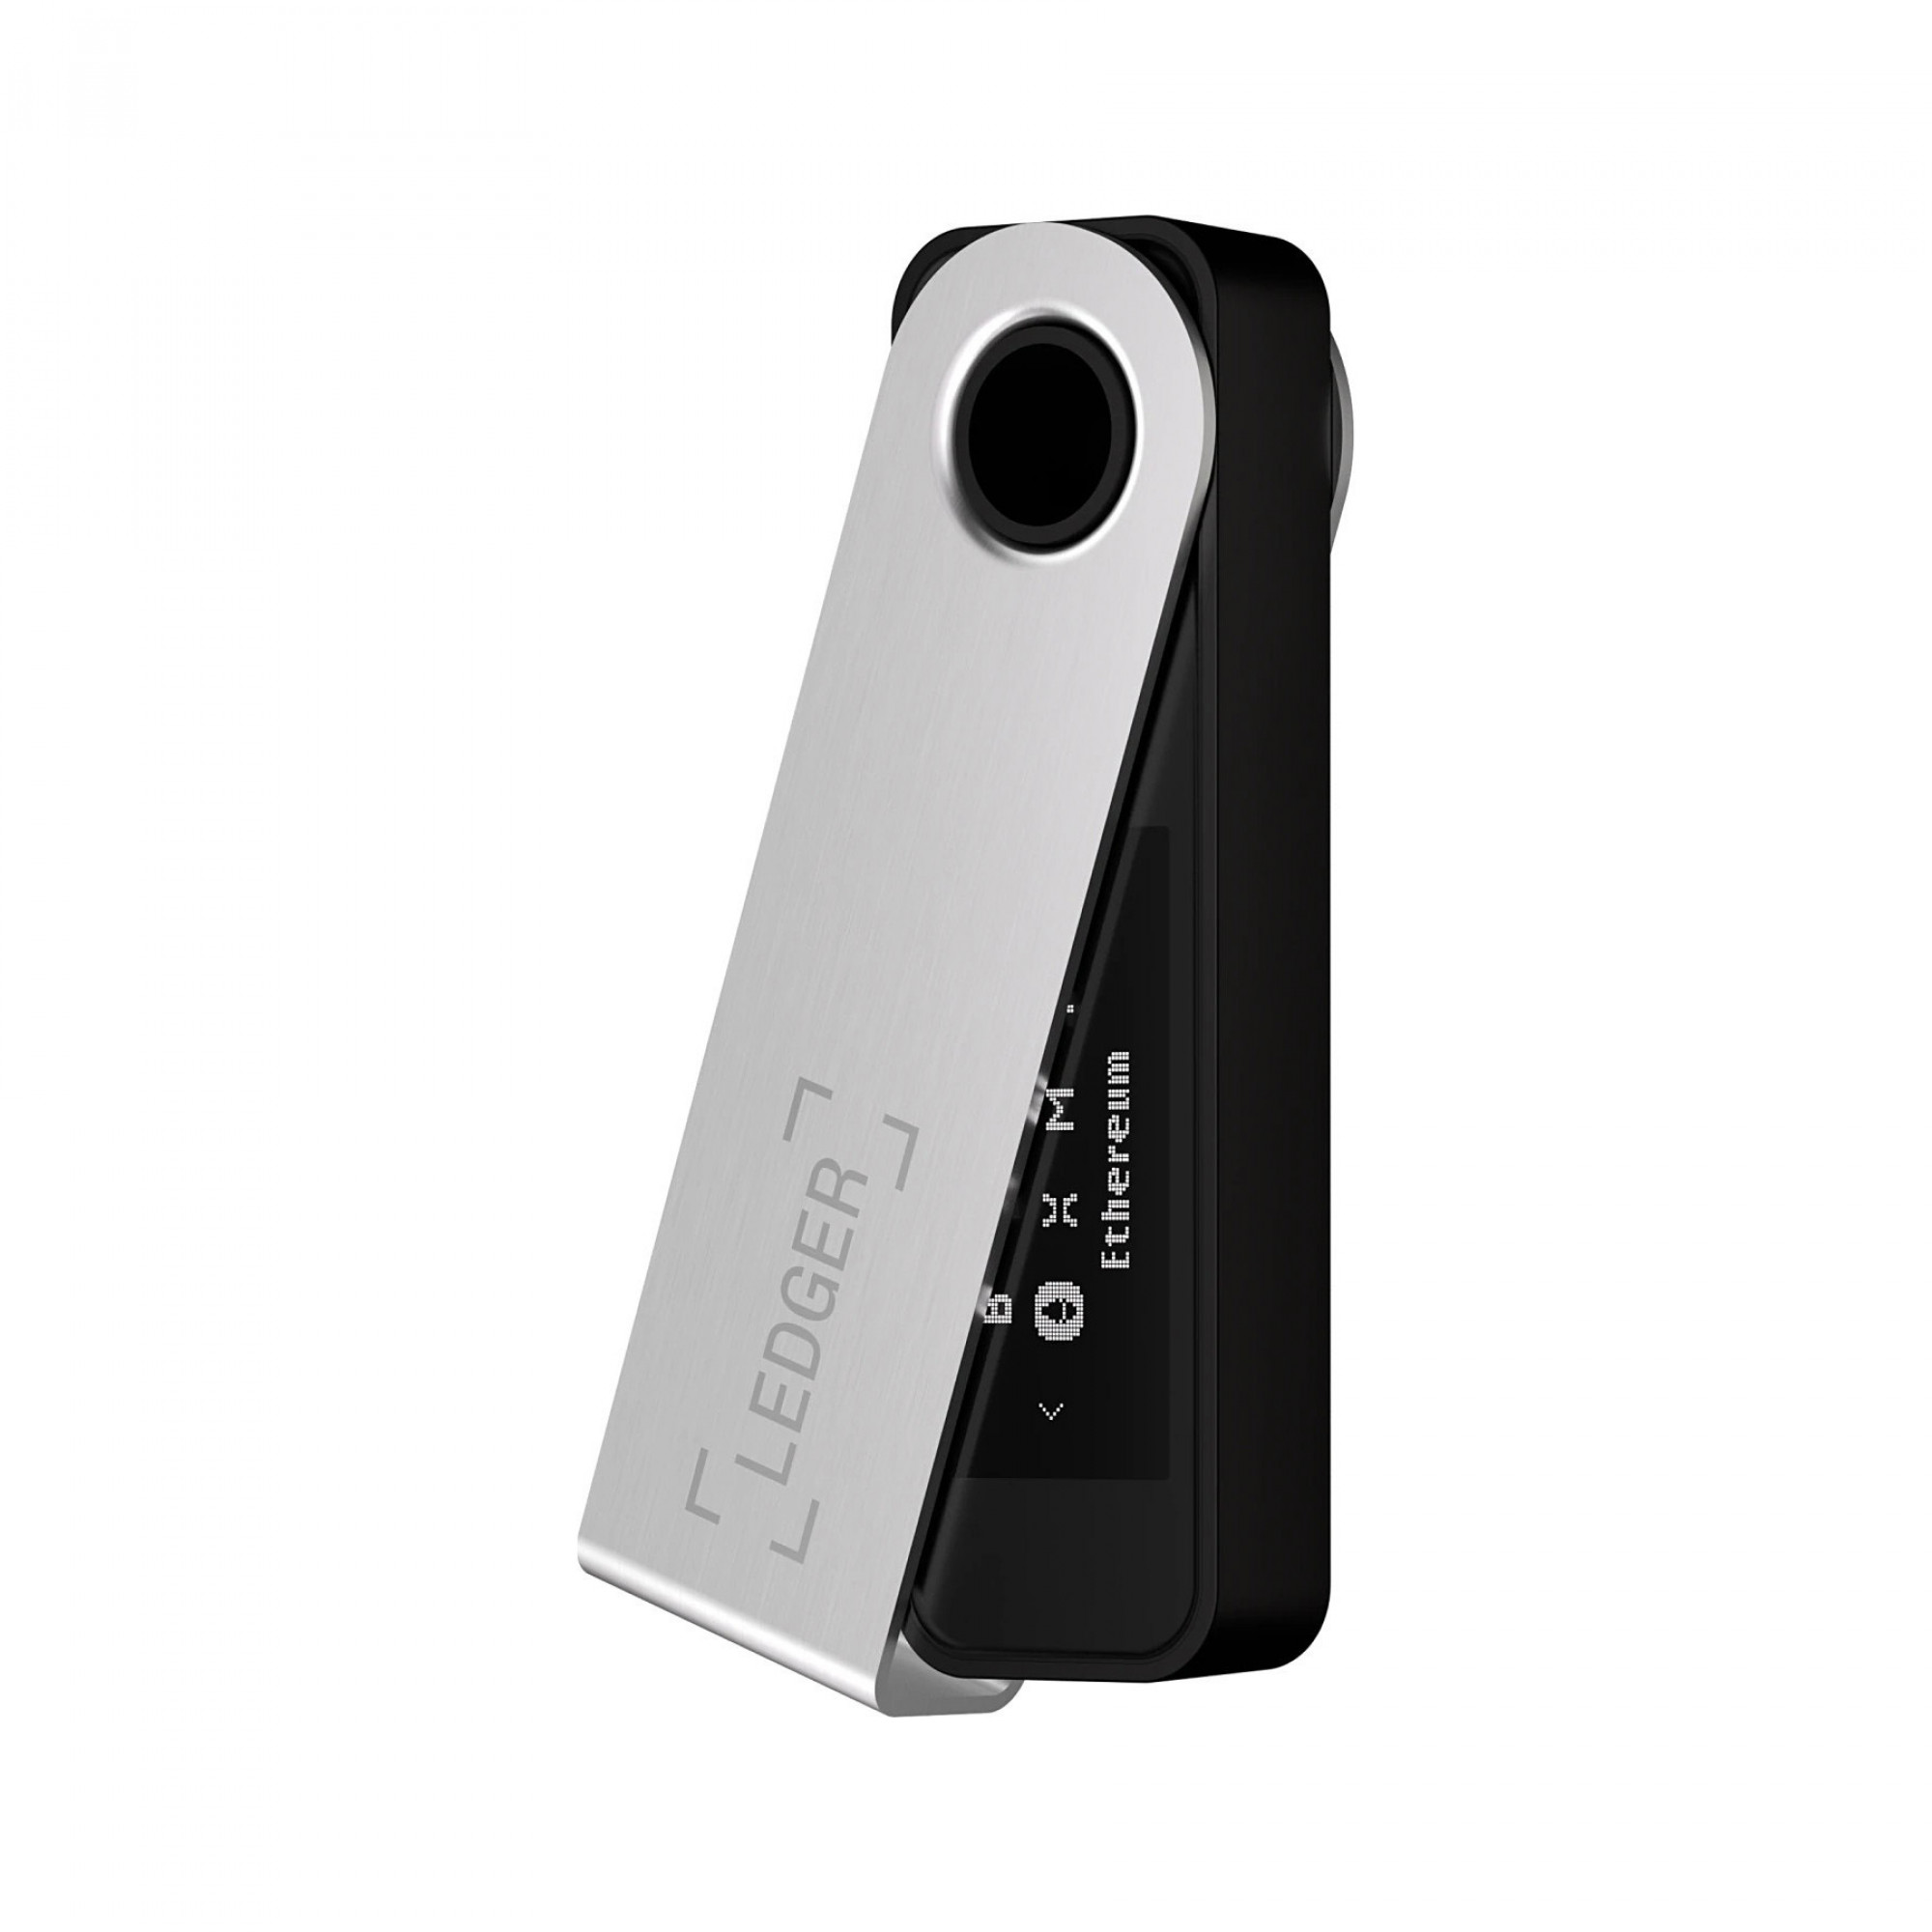
The discovery of the modified devices follows reports of suspicious activity among customers in Indonesia, Malaysia, and the Philippines. Security researcher Mark Karpelès initially identified a hidden electronic component behind the screen of a Ledger Nano X, which appeared to include a microcontroller and cellular communication capabilities. Technical analysis suggests this hardware could potentially intercept recovery phrases during the device initialization process, though Ledger has not confirmed this as the specific mechanism behind the reported losses.
CryptoBilis has suspended all hardware wallet sales while cooperating with the investigation. Ledger maintains that its internal security systems remain uncompromised, emphasizing that the issue is isolated to physical tampering at the distribution level. The company is currently contacting affected users and advising those with suspicious devices to abandon their current recovery phrases in favor of new, securely generated credentials. While blockchain analytics firm Bitquery estimates that 311 wallets have been drained of approximately $92.9 million, Ledger has not verified these figures or confirmed the identity of the perpetrators behind the supply chain breach.
Comments (0)
No comments yet. Be the first!