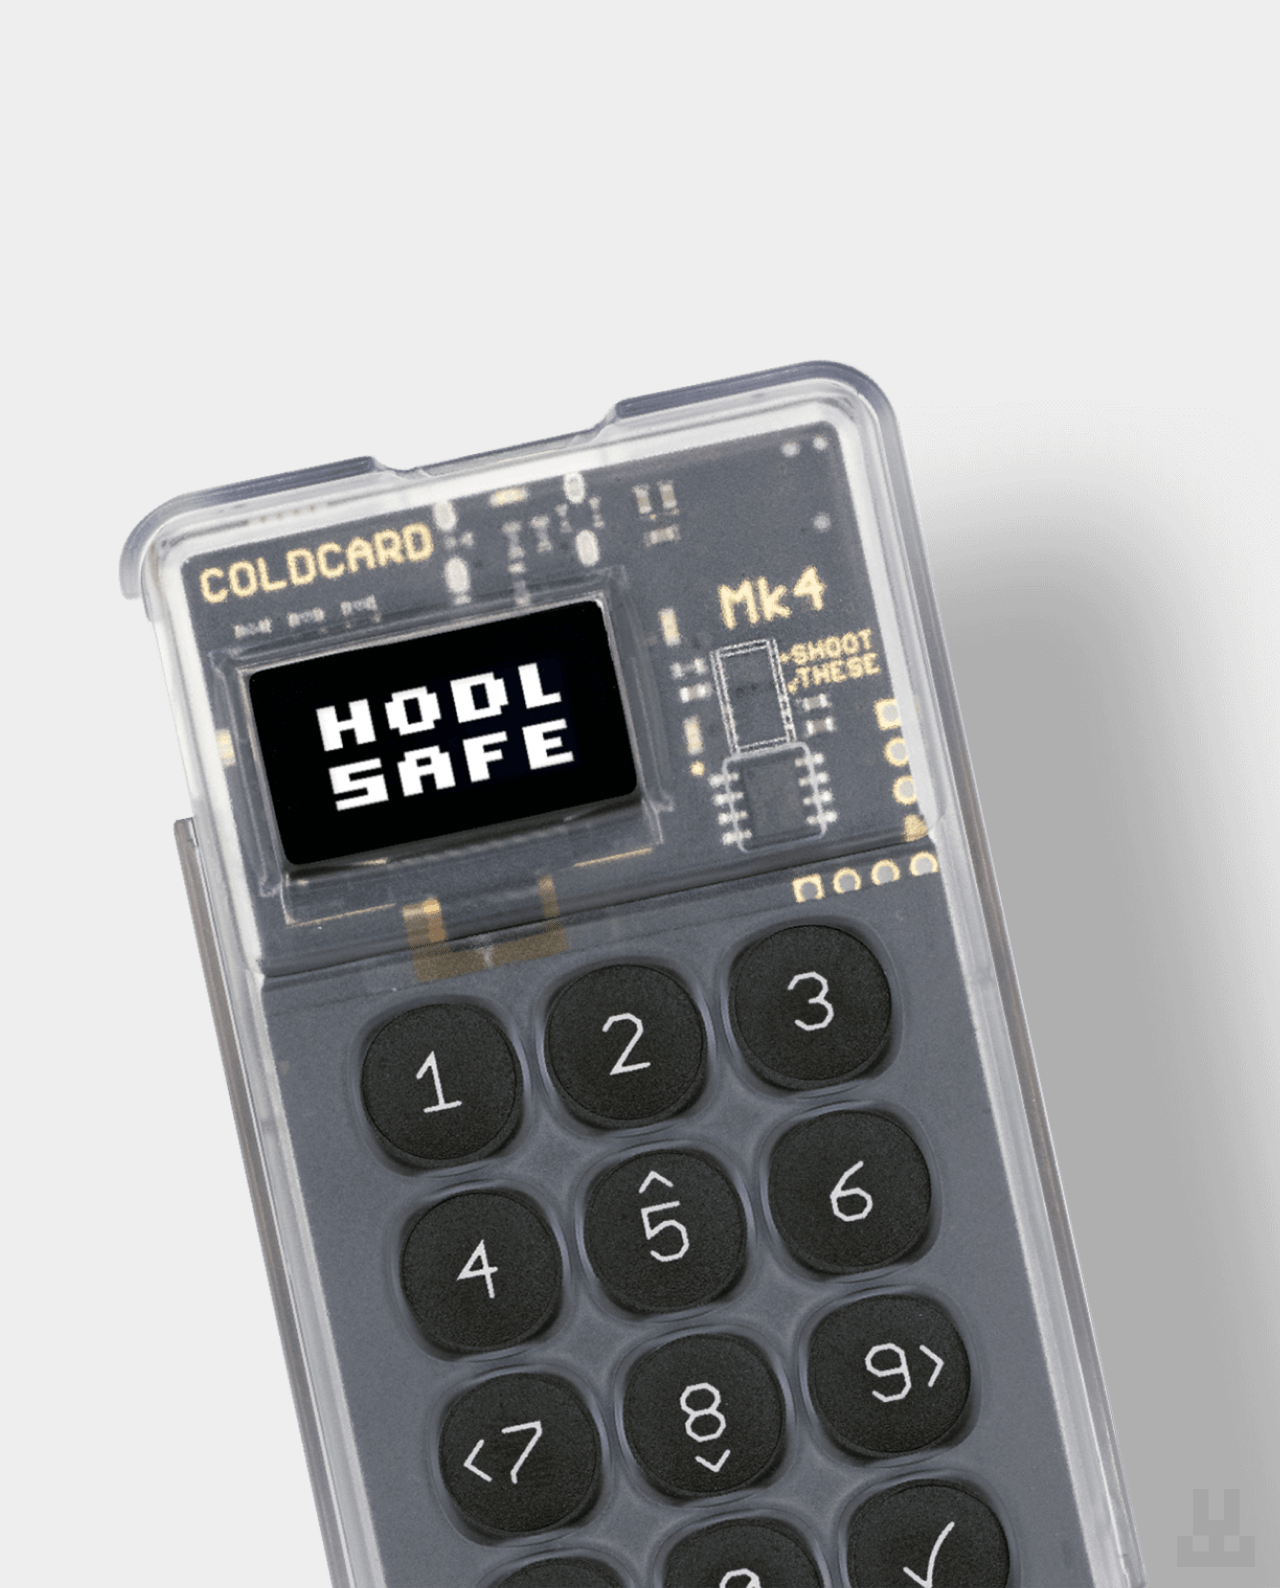
The company deleted the post shortly after discovery and confirmed that no legitimate firmware updates were associated with the warning. While investigators are currently reviewing account access logs, COLDCARD reported that it found no evidence of a standard login or session match. The firm maintains that it has utilized offline two-factor authentication and restricted access protocols since 2017, leading it to query X regarding potential platform-level vulnerabilities or administrative bypasses.
Security and Impersonation Risks
COLDCARD has emphasized that its only legitimate web portal is coldcard.com and warned customers against interacting with any external links claiming to facilitate wallet migrations. This incident follows a series of widespread impersonation attempts documented since July, when the manufacturer disclosed a genuine firmware issue related to recovery phrase randomness. Cybersecurity researchers have previously identified dozens of fraudulent accounts and domains attempting to harvest user data by mimicking official support channels. Despite the sophistication of these campaigns, the manufacturer stated that no verified financial losses have been linked to the October 11 social media breach. The company continues to coordinate with X to determine how the account was compromised without triggering standard security alerts.
Comments (0)
No comments yet. Be the first!